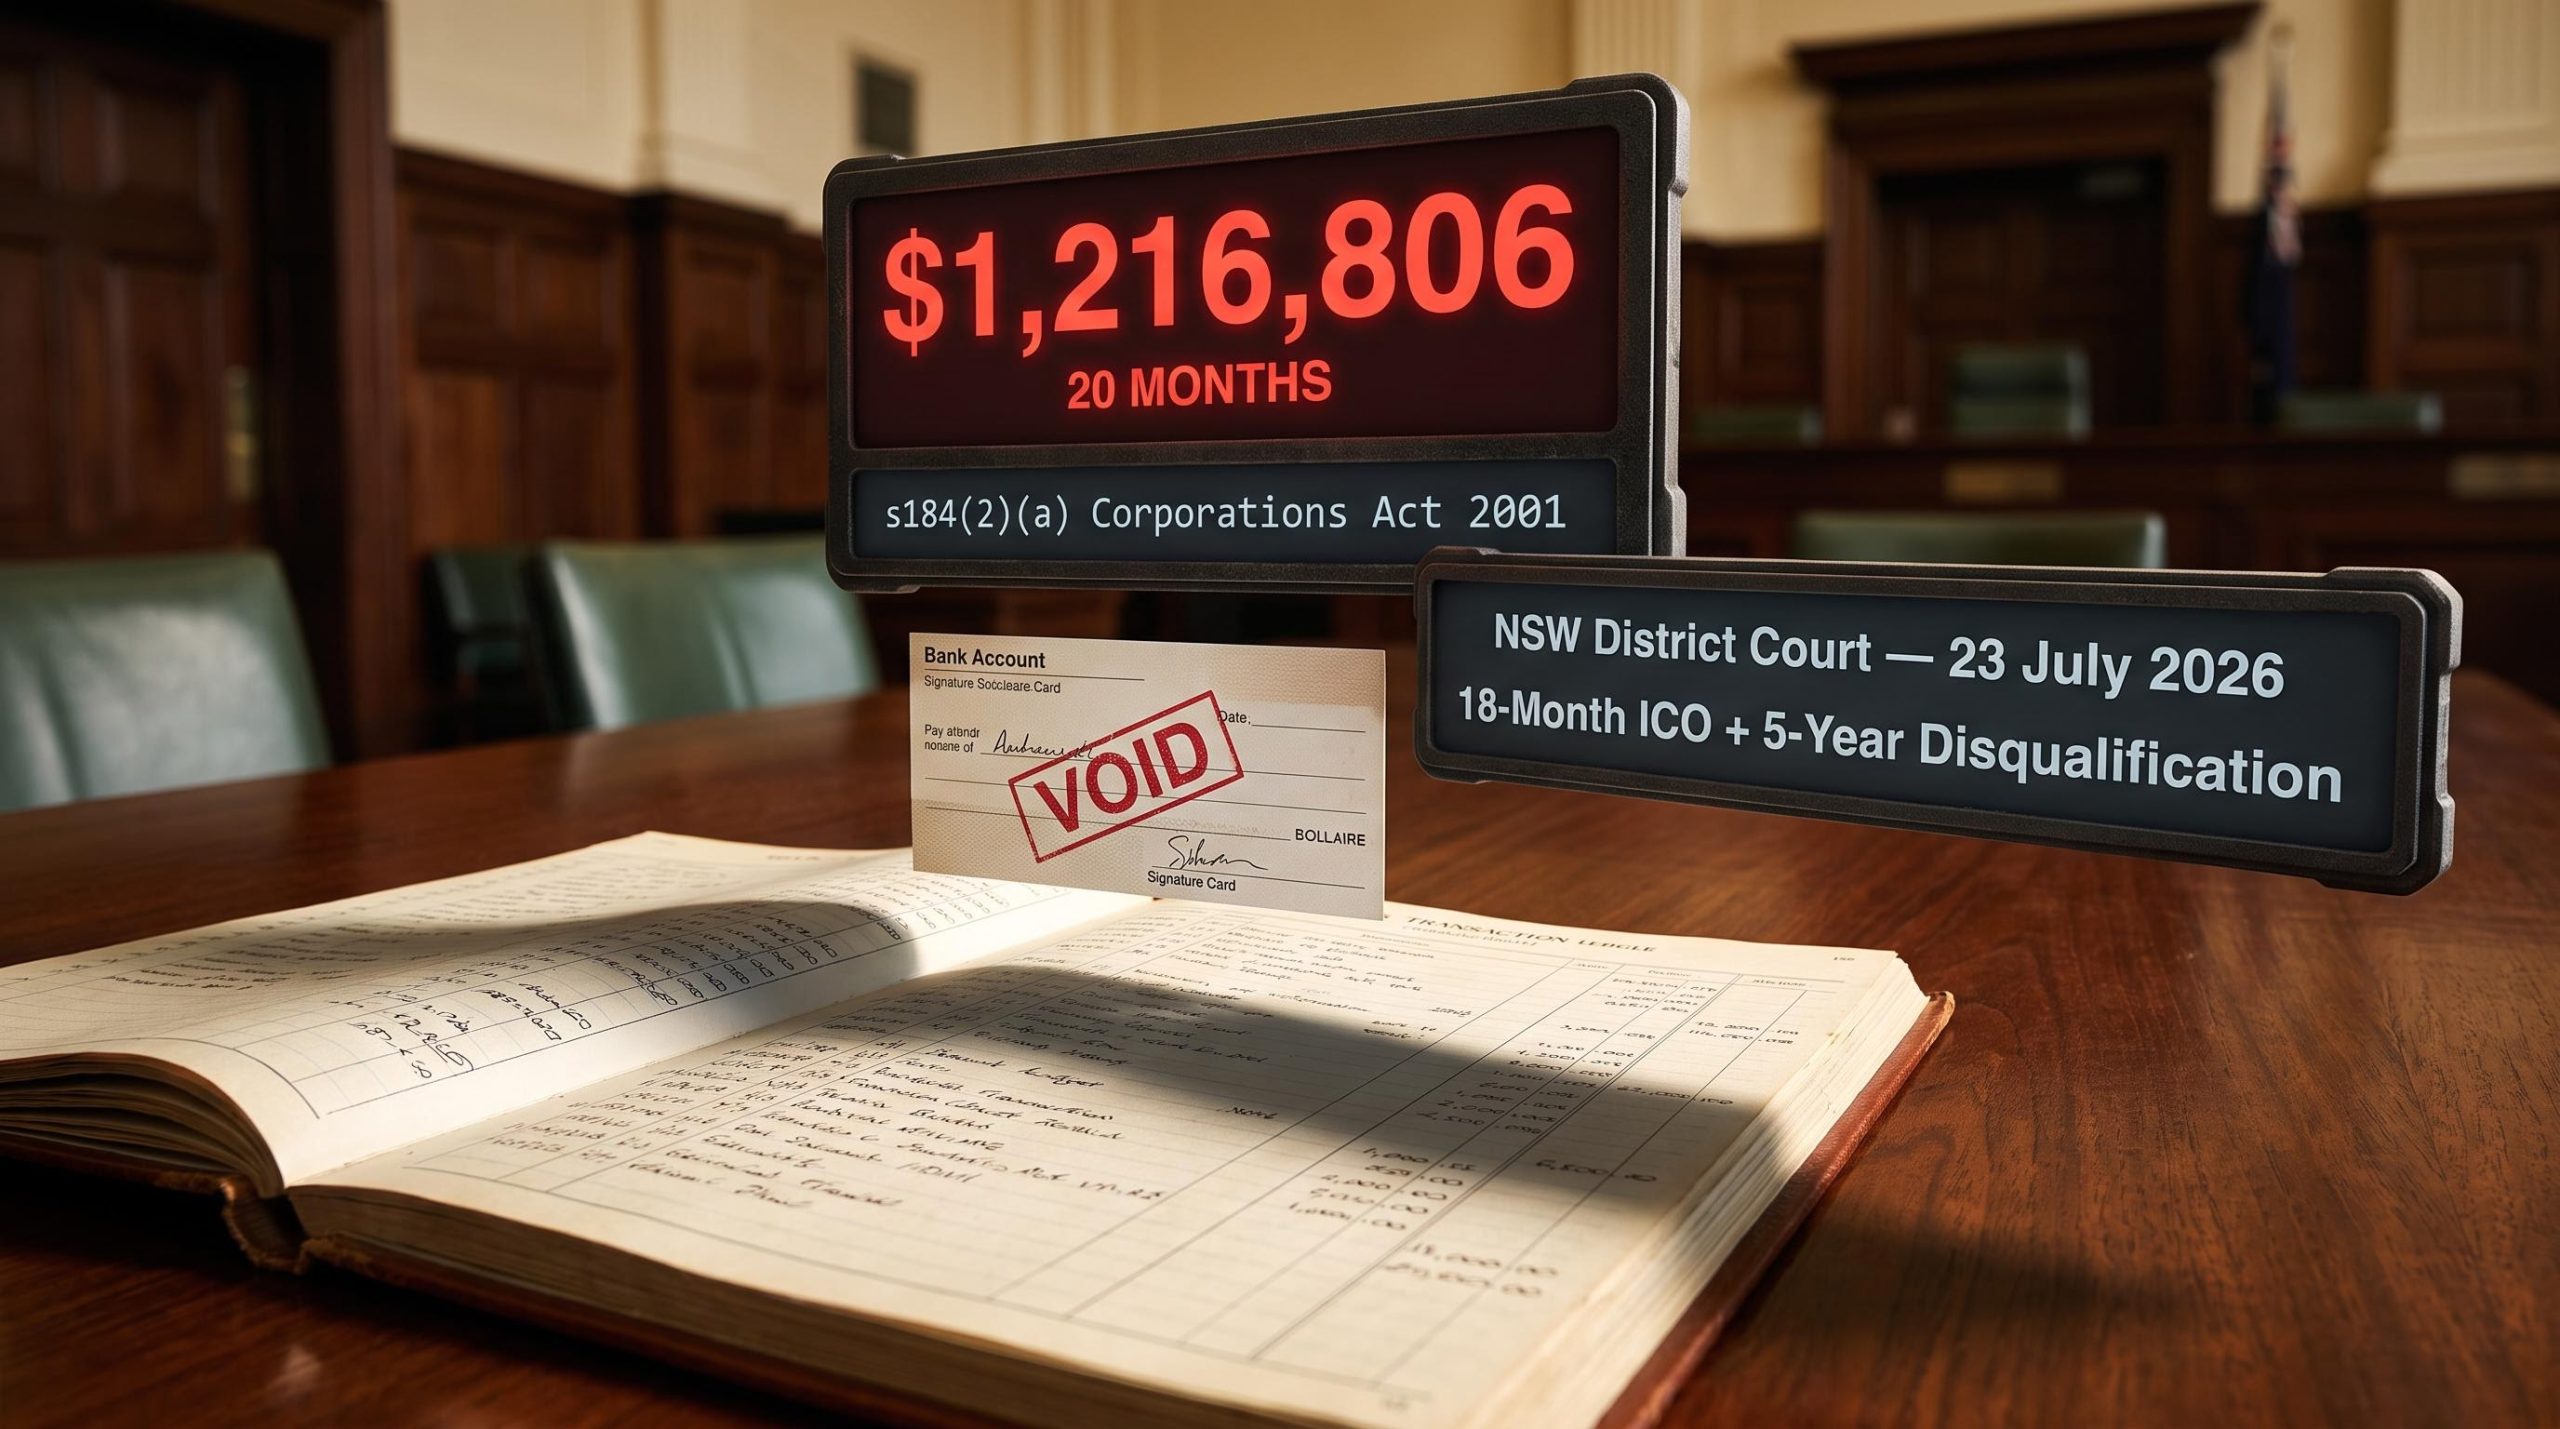
A NSW construction sector director received an 18-month Intensive Corrections Order last week after draining $1,216,806 from two companies she controlled. The mechanism was not sophisticated. Operating as the exclusive authoriser for the bank accounts of both firms, Vickie Anne Vella exploited this lack of oversight across a period of 20 months to pay for personal entertainment, pull out cash, and cover private memberships, entirely bypassing any need for a second signature.
The conviction, recorded on 23 July 2026 in the NSW District Court, matters beyond the individual case. The same governance weakness that made this fraud possible, a single person with sole control over company cash and no dual-signatory requirement, exists across thousands of Australian SMEs today. ASIC and the Commonwealth Director of Public Prosecutions (CDPP) are now consistently treating these structural failures as criminal enforcement opportunities.
Here is what the court established, what automatic disqualification means in practice, and which specific controls would have broken this fraud before it ran for nearly two years. If you sit on a board, invest in private companies, or operate a business where one director controls the bank account, this is directly relevant.
How a NSW director siphoned $1.2 million through a single bank account
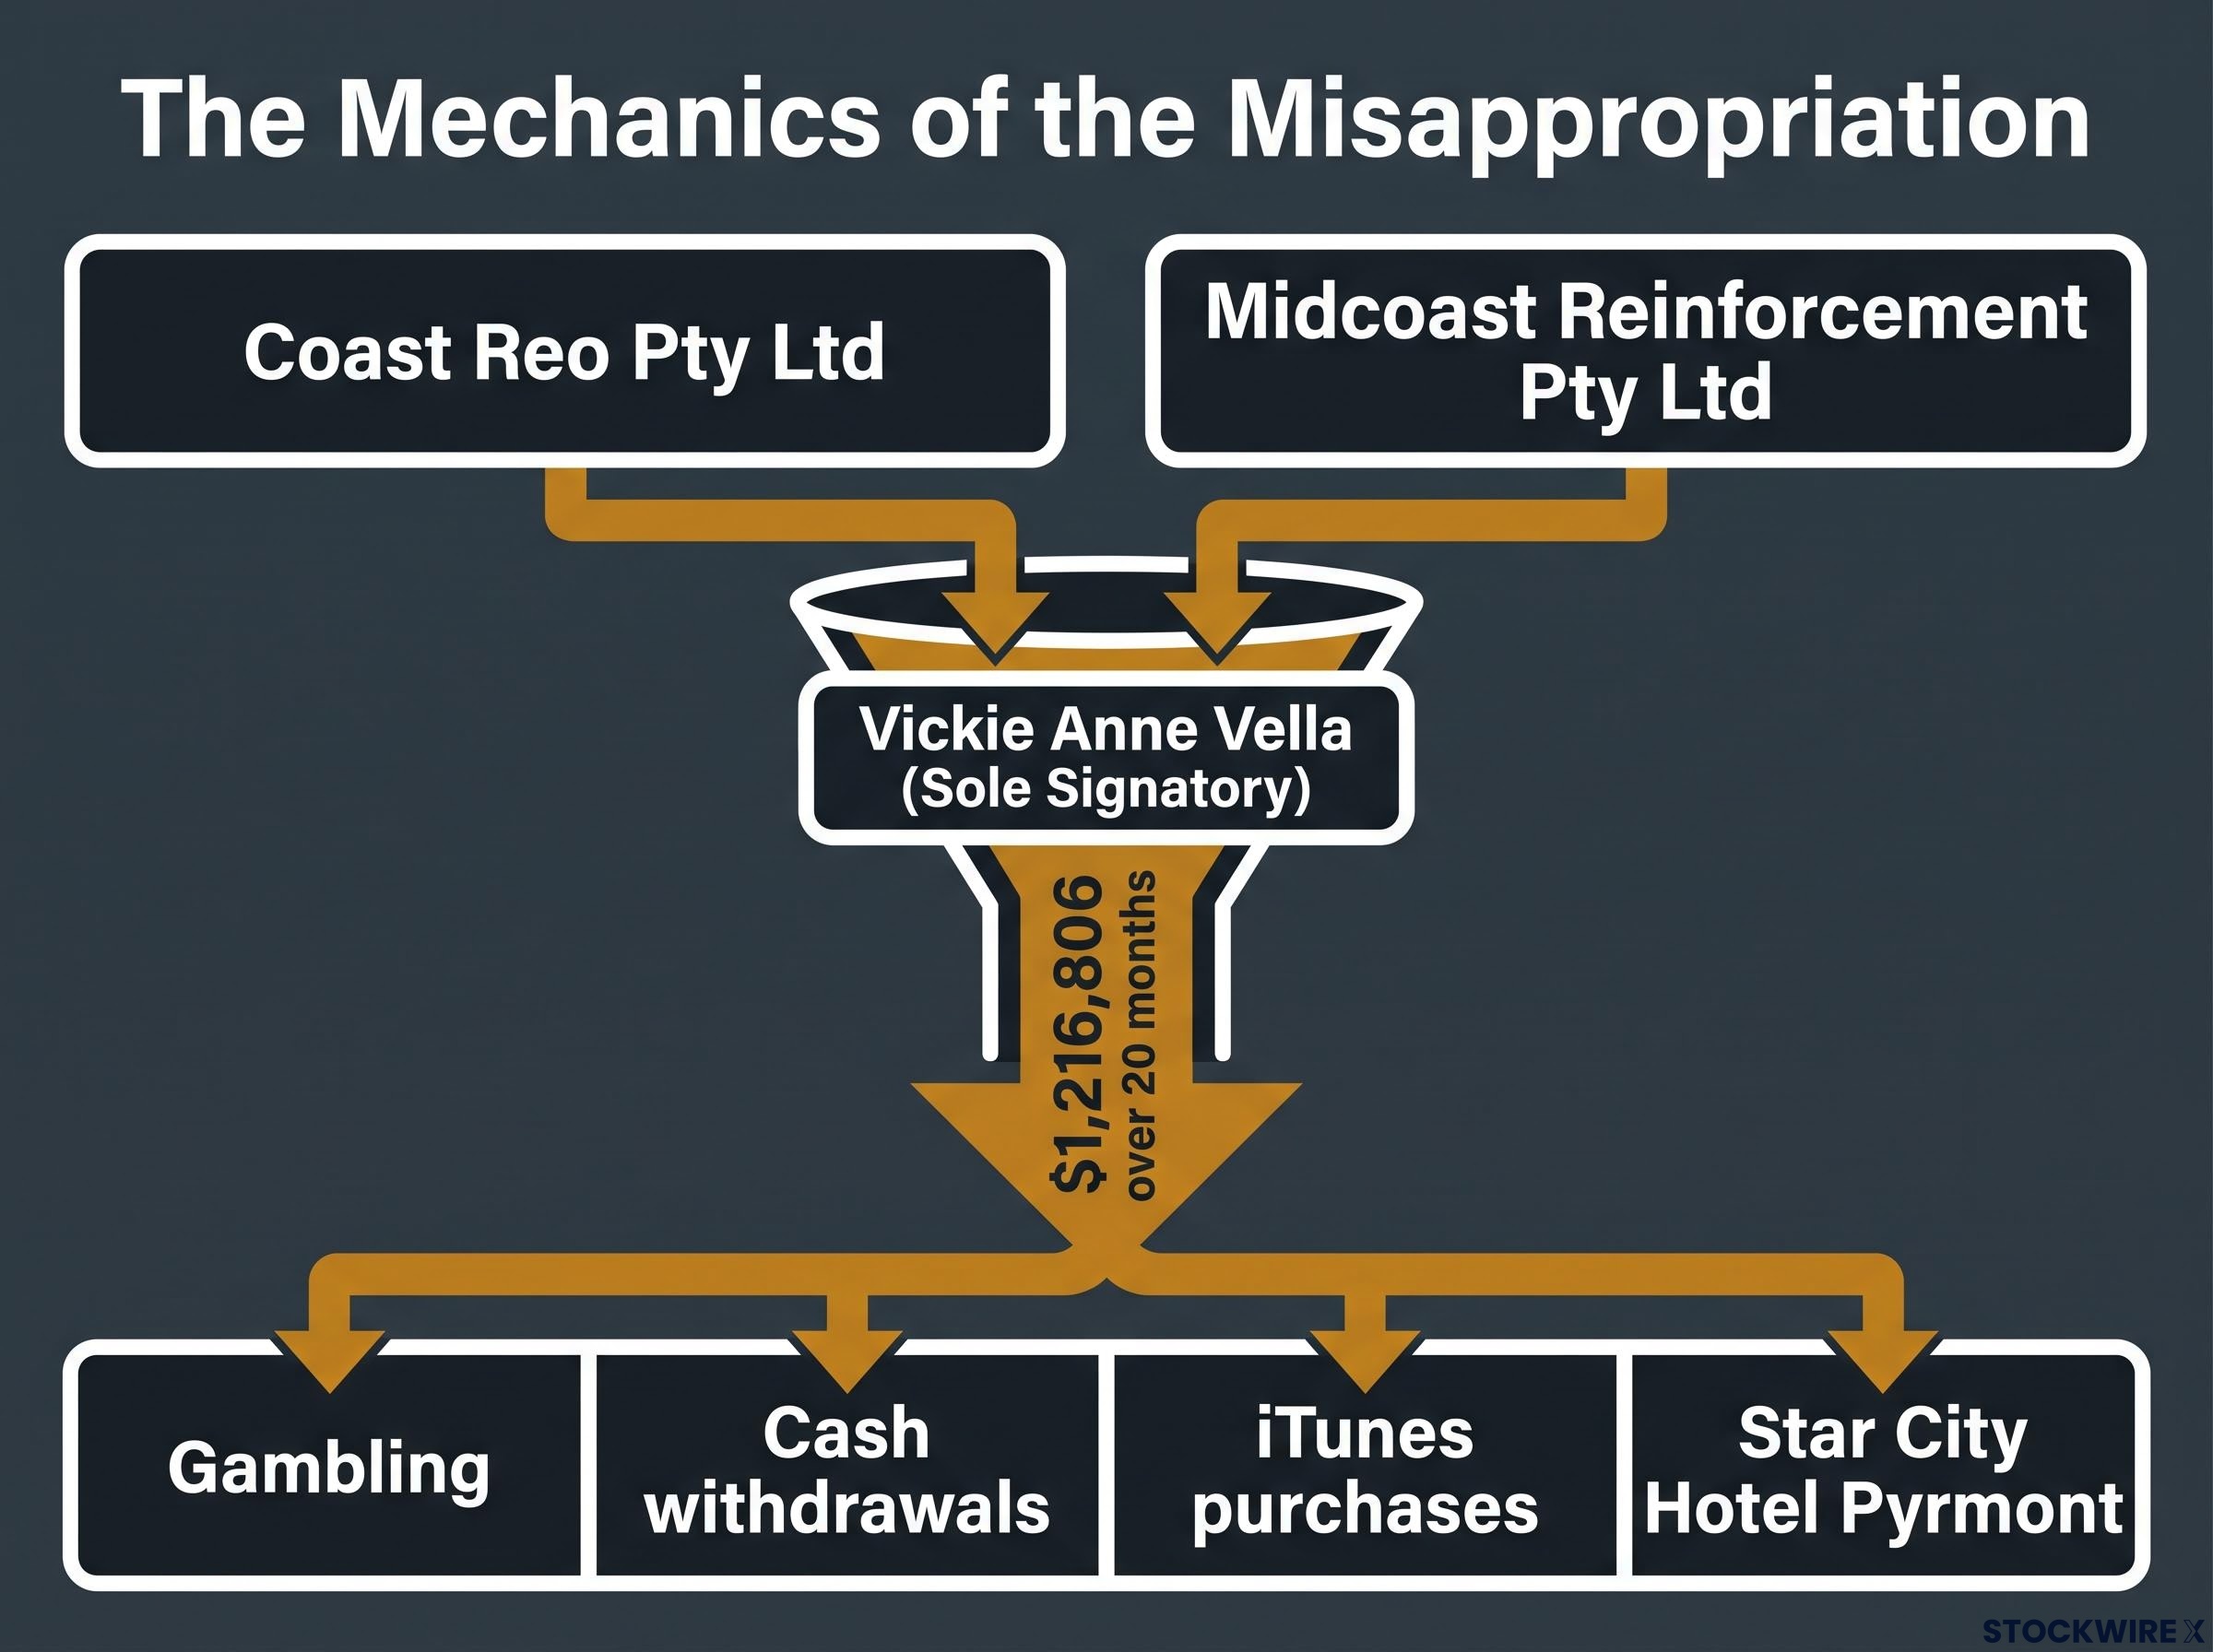
Vella previously served as a director for two connected building materials providers, Coast Reo Pty Ltd and Midcoast Reinforcement Pty Ltd, which operated throughout regional NSW under the names Newcastle Plastamasta, Central Coast Plastamasta, and Port Macquarie Plastamasta. On 10 April 2026, she admitted guilt to a single count of violating s184(2)(a) of the Corporations Act 2001 (Cth), which involved fraudulently leveraging her corporate role to secure a benefit or inflict harm.
The companies involved
The two entities distributed metal and plasterboard materials to clients situated in the Port Macquarie and Central Coast areas. The two firms fell into liquidation in 2018, the same year the offending period ended.
The mechanics of the withdrawals
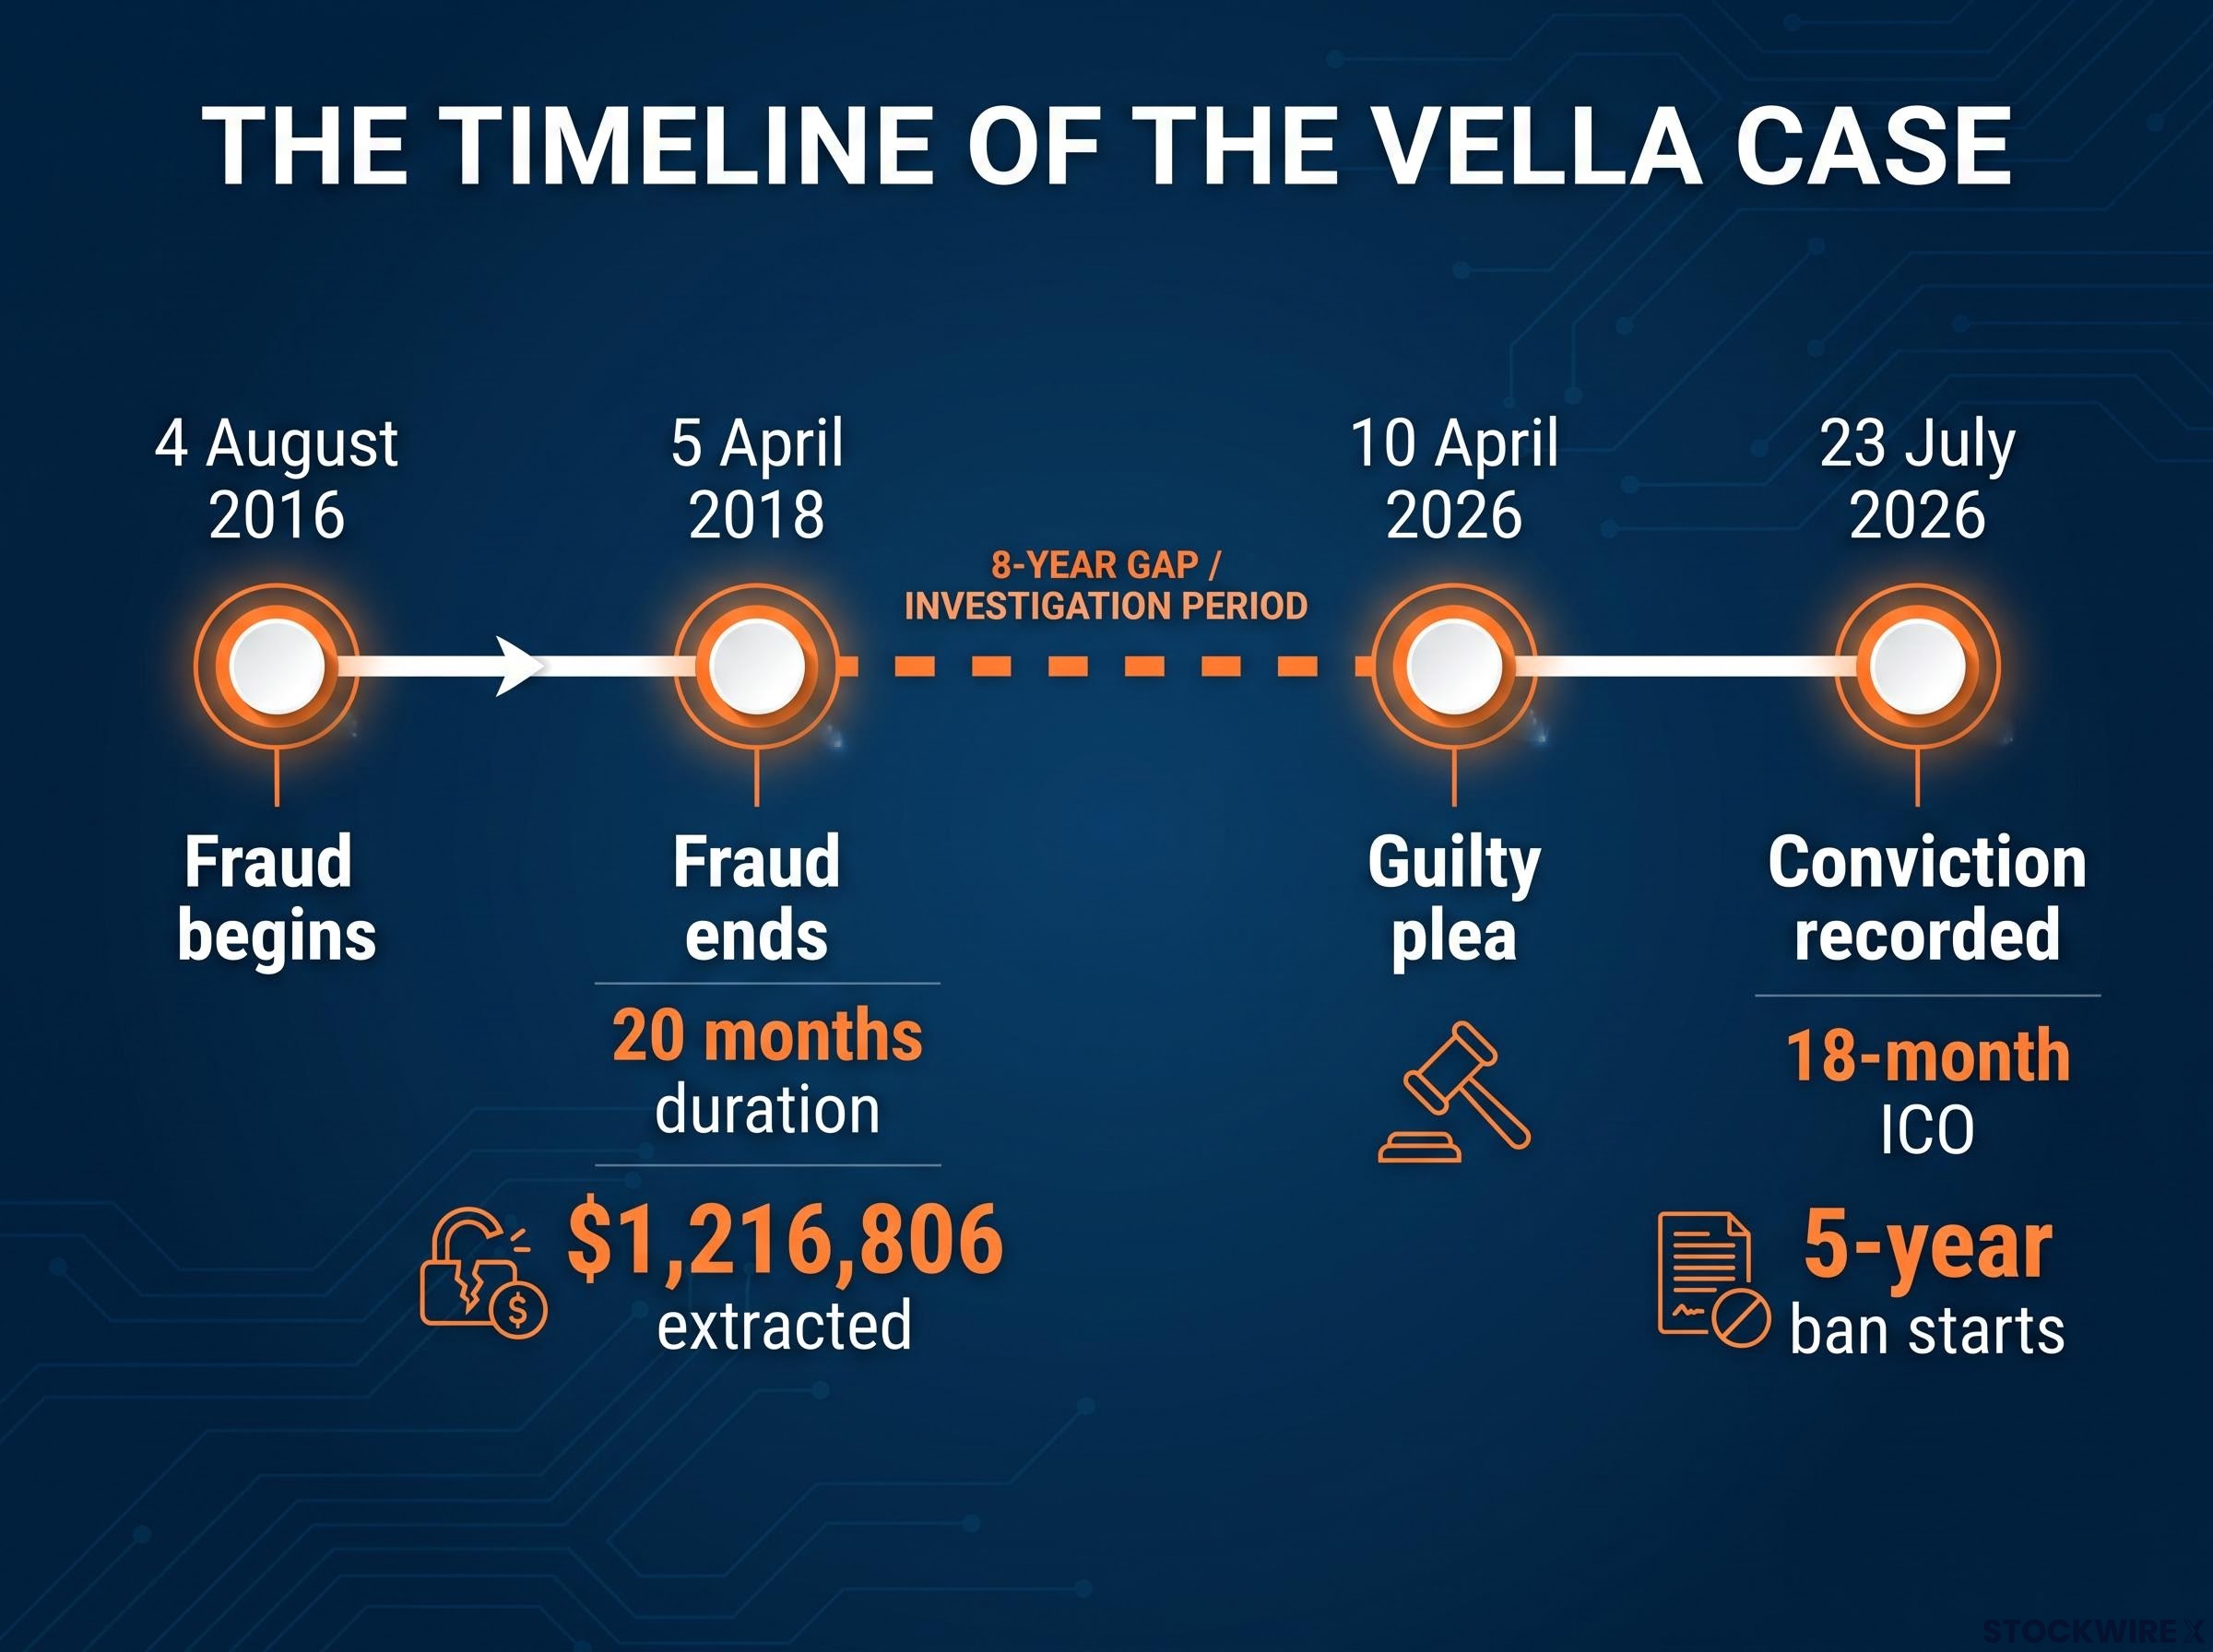
From 4 August 2016 to 5 April 2018, Vella extracted roughly $1,216,806 out of corporate funds, funnelling the money into private costs such as:
- Gambling
- Cash withdrawals
- iTunes purchases
- Star City Hotel Pyrmont subscriptions
None of these expenses related to company business. The mechanism required no concealment technology, no falsified invoices, and no collusion. For the financial accounts of both entities, Vella held sole signatory powers. No co-authorisation existed to catch or delay a single withdrawal. The structural weakness was sufficient on its own, and that same arrangement remains unremarkable across Australian SMEs today.
When big ASX news breaks, our subscribers know first
What the court said, and what the sentence actually means
District Court Judge Smith handed down a penalty of 18 months’ imprisonment on 23 July 2026, directing that the term be completed under an Intensive Corrections Order (ICO), a supervised community-based sentence that replaces full-time custody but carries the same criminal conviction record and legal consequences.
When the breaches occurred, the most severe punishment possible included 5 years’ imprisonment, a fine of 2,000 penalty units (amounting to $360,000 at the time), or a combination of the two.
Judge Smith noted that general deterrence carried considerable weight in sentencing, specifically to discourage individuals of seemingly good character from exploiting positions of trust.
That judicial language is pointed. The court is not describing career criminals. It is describing people who hold director positions, enjoy community standing, and use that trust as cover. The explicit focus on deterring “individuals of seemingly good character” signals that ASIC and the CDPP regard trusted operators who misuse their positions as priority enforcement targets, not marginal ones.
Corporate management bans explained: how disqualification works under the Corporations Act
As a direct consequence of the court’s finding, Vella received an automatic five-year ban prohibiting her from corporate management roles, effective from 23 July 2026 to 23 July 2031. This is not a discretionary penalty or a separate ASIC decision. It is a statutory consequence under the Corporations Act: a person convicted of certain dishonesty offences involving director duties is automatically disqualified. No additional regulatory action is required.
During this period, Vella cannot lawfully manage, participate in management, or act as a director of any Australian corporation.
The automatic disqualification Vella received is one pathway; ASIC director disqualification under Section 206F can also be triggered administratively, without a court order or criminal conviction, when a person has been an officer of multiple wound-up companies within a seven-year period.
The outcome is consistent with comparable cases ASIC has pursued:
| Director | Amount | Sentence | Disqualification |
|---|---|---|---|
| Vickie Anne Vella (Coast Reo / Midcoast Reinforcement) | $1,216,806 | 18 months (ICO) | 5 years (automatic) |
| George Nowak (Charterhill Group) | $1.2 million (SMSF) | 10 years’ imprisonment | 5 years (automatic) |
| Anthony Torre | Over $1 million (superannuation) | Custodial sentence | 5 years (automatic) |
For anyone currently serving as a co-director alongside someone under investigation, or investing in a company with governance concerns, checking ASIC’s registers is not optional due diligence. Allowing a disqualified person to participate in management can itself trigger enforcement action. The register is publicly accessible, and boards have an obligation to verify.
Why sole signatory authority is a governance red flag
Why sole signatory arrangements create structural risk
A sole signatory arrangement means one person can authorise payments from a company bank account without any second party approving, reviewing, or even seeing the transaction. In SMEs, this is common. Informal trust between founders or co-directors often substitutes for formal controls, particularly in family-run or regional businesses where relationships feel like sufficient safeguards.
The risk is straightforward: there is no contemporaneous scrutiny of withdrawals, no second-party authorisation requirement, and no structural mechanism that forces visibility. In multi-entity structures like Vella’s, the risk multiplies because the same unchecked authority extends across multiple sets of company funds simultaneously.
The Vella fraud ran for approximately 20 months. Both companies entered liquidation the same year it ended. The absence of controls is not simply an efficiency gap. Courts, regulators, and liquidators will treat it as a governance failure after the fact.
For investors, the link between corporate governance controls and company valuation is not abstract: research on newly listed companies shows that governance quality compounds into measurable valuation outcomes over the first eight to twelve quarters, with the absence of oversight structures a persistent drag long before any misconduct surfaces.
Controls that break the pattern
Four specific controls would have disrupted or prevented the Vella fraud:
- Dual authorisation thresholds: Require two signatories for any payment above a defined amount, ensuring no single individual can move material sums unilaterally
- Segregation of duties: Separate the roles of payment approval, payment execution, and bank statement reconciliation across different people
- Independent bank reconciliation: Mandate monthly or quarterly reconciliation reviews conducted by someone independent of day-to-day payment processing, such as an external accountant
- Direct board visibility of bank data: Provide the board with access to bank-level transaction data, not just management-prepared profit-and-loss summaries
For multi-entity structures, each entity should have its own clear oversight mechanisms. Cross-entity cash movements should be independently documented and reviewed.
ASIC’s enforcement posture: why trusted insiders are now a prosecution priority
The Vella conviction fits a deliberate pattern. ASIC and the CDPP are consistently pursuing directors and financial controllers who misuse positions of trust over company funds, across industries and company sizes.
The conduct in Vella’s case ran from 2016 to 2018. The guilty plea came in April 2026. The conviction was recorded in July 2026, approximately eight years after the offending began.
That timeline should recalibrate any assumption that time reduces legal exposure. For dishonesty offences under the Corporations Act, ASIC maintains investigative files well beyond the conduct period. The passage of time did not protect Vella, and it has not protected others.
Common themes across ASIC’s enforcement in this area:
- Trusted insider status is treated as an aggravating factor, not a mitigating one
- Investigations span years and are pursued through corporate collapses and liquidations
- The CDPP is regularly engaged, signalling that serious director misconduct is criminal behaviour warranting custodial sentences, not merely civil penalties
- Construction SMEs, regional businesses, and companies without formal governance infrastructure are demonstrably within scope
George Nowak of the Charterhill Group misappropriated $1.2 million in self-managed superannuation fund money and received 10 years’ imprisonment. These are not isolated outcomes. They are an enforcement posture.
The Hilellis case, in which ASIC imposed the maximum administrative ban following four corporate collapses in the construction and security sectors, illustrates that administrative disqualification and criminal conviction operate as parallel enforcement tracks, each with independent penalty ceilings.
What this conviction changes for directors and investors in 2026
The Vella case sends a dual message. For directors, the legal risk of exploiting unchecked financial control is being treated by the judiciary as a general deterrence opportunity, with explicit intent to influence the behaviour of every person in a comparable position. For investors, the governance red flags this case illustrates are identifiable before a fraud runs for 20 months.
Seven due diligence questions you can apply to any company you are connected to:
- Who are the authorised signatories on all company bank accounts, and is any person a sole signatory on any account?
- Are there transaction thresholds that trigger dual approval or automatic escalation?
- How frequently are bank reconciliations reviewed by someone independent of day-to-day payment processing?
- In multi-entity structures, does each entity have clear governance and oversight rather than centralising everything in one individual?
- Does the board receive transparent reporting of cash movements, not merely profit-and-loss statements?
- Are there whistleblower and incident-reporting mechanisms that stakeholders feel confident using?
- Have the ASIC registers been checked to confirm that no director or manager is currently disqualified from managing corporations?
The Corporations Act treats director positions as positions of legally enforceable trust. The Vella conviction confirms that serious breaches will be pursued criminally, not merely civilly, and that the governance controls outlined above are not aspirational best practice. They are the minimum structural threshold the regulatory environment now implies.
For investors wanting a structured framework to apply the seven due diligence questions above, our dedicated guide to evaluating small-cap management covers the red flag stacking approach, per-share return analysis, and insider ownership signals that professional investors use to assess management quality before governance failures become public.
This article is for informational purposes only and should not be considered financial advice. Investors should conduct their own research and consult with financial professionals before making investment decisions.