Manufacturers with a household name are not the ones most exposed to ransomware. The median victim has roughly $42.9 million in annual revenue, and in Germany the number of manufacturing victims has climbed to nearly double last year’s pace.
Manufacturing has topped ransomware target lists for four straight years, according to Black Kite, a third-party cyber risk firm. The first seven months of 2026 produced 1,183 manufacturing victims, more than in all of 2024.
The risk is moving away from the large-cap US industrials many investors watch. Here is a way to read exposure in an industrial portfolio, and in the suppliers behind it.
Is the surge structural or just a few groups making noise?
The headline numbers are hard to wave away. Manufacturing made up 22% of 7,551 publicly disclosed ransomware victims across all sectors in Black Kite’s dataset, and attacks have more than doubled since 2023. Volume in the first seven months of 2026 was up 39.7% year on year.
Dragos, which tracks industrial and operational technology (OT) threats, tells a similar story. Ransomware groups targeting industrial organisations rose 49%, affecting 3,300 organisations, and manufacturing accounted for 62-65% of industrial incidents in the first half of 2026.
| Tracker | Scope | Key 2026 figure | Data basis |
|---|---|---|---|
| Black Kite | All sectors | 1,183 manufacturing victims in seven months, up 39.7% | Disclosed and claimed victims |
| Dragos | Industrial organisations | 1,020 incidents in Q1 2026, 1,140 in Q2 2026 (up 12%) | Disclosed victims and leak-site postings |
| Verizon DBIR | Breaches in manufacturing | Ransomware in 61% of breaches | Breach investigations |
Why the numbers differ between trackers
Black Kite’s 22% and Dragos’s two-thirds do not conflict. One measures manufacturing against every sector; the other measures it only against industrial organisations.
Every tracker also leans on leak sites, where criminals post victims’ data. Companies that pay quietly never appear, while groups can double-claim or exaggerate, and high-publicity gangs may be over-represented.
The structural case is strong: multi-year doubling, plus Dragos’s “fundamental shift” framing. The cyclical case is real too, since The Gentlemen jumped from 18 to 83 incidents in a single quarter.
What this tells you is that the direction of travel is reliable while any single count is not. Rest your judgement on the trend, not one tracker’s figure.
When big ASX news breaks, our subscribers know first
What makes a factory such a profitable target?
Start from the attacker’s side. A stolen database is worth something, but a halted production line costs the victim money every hour, and that is where the leverage sits.
Operational technology (OT) means the hardware and software that run physical processes, such as machinery and assembly lines. Ordinary IT handles email, files and payroll. When IT goes down, work slows; when OT goes down, output stops.
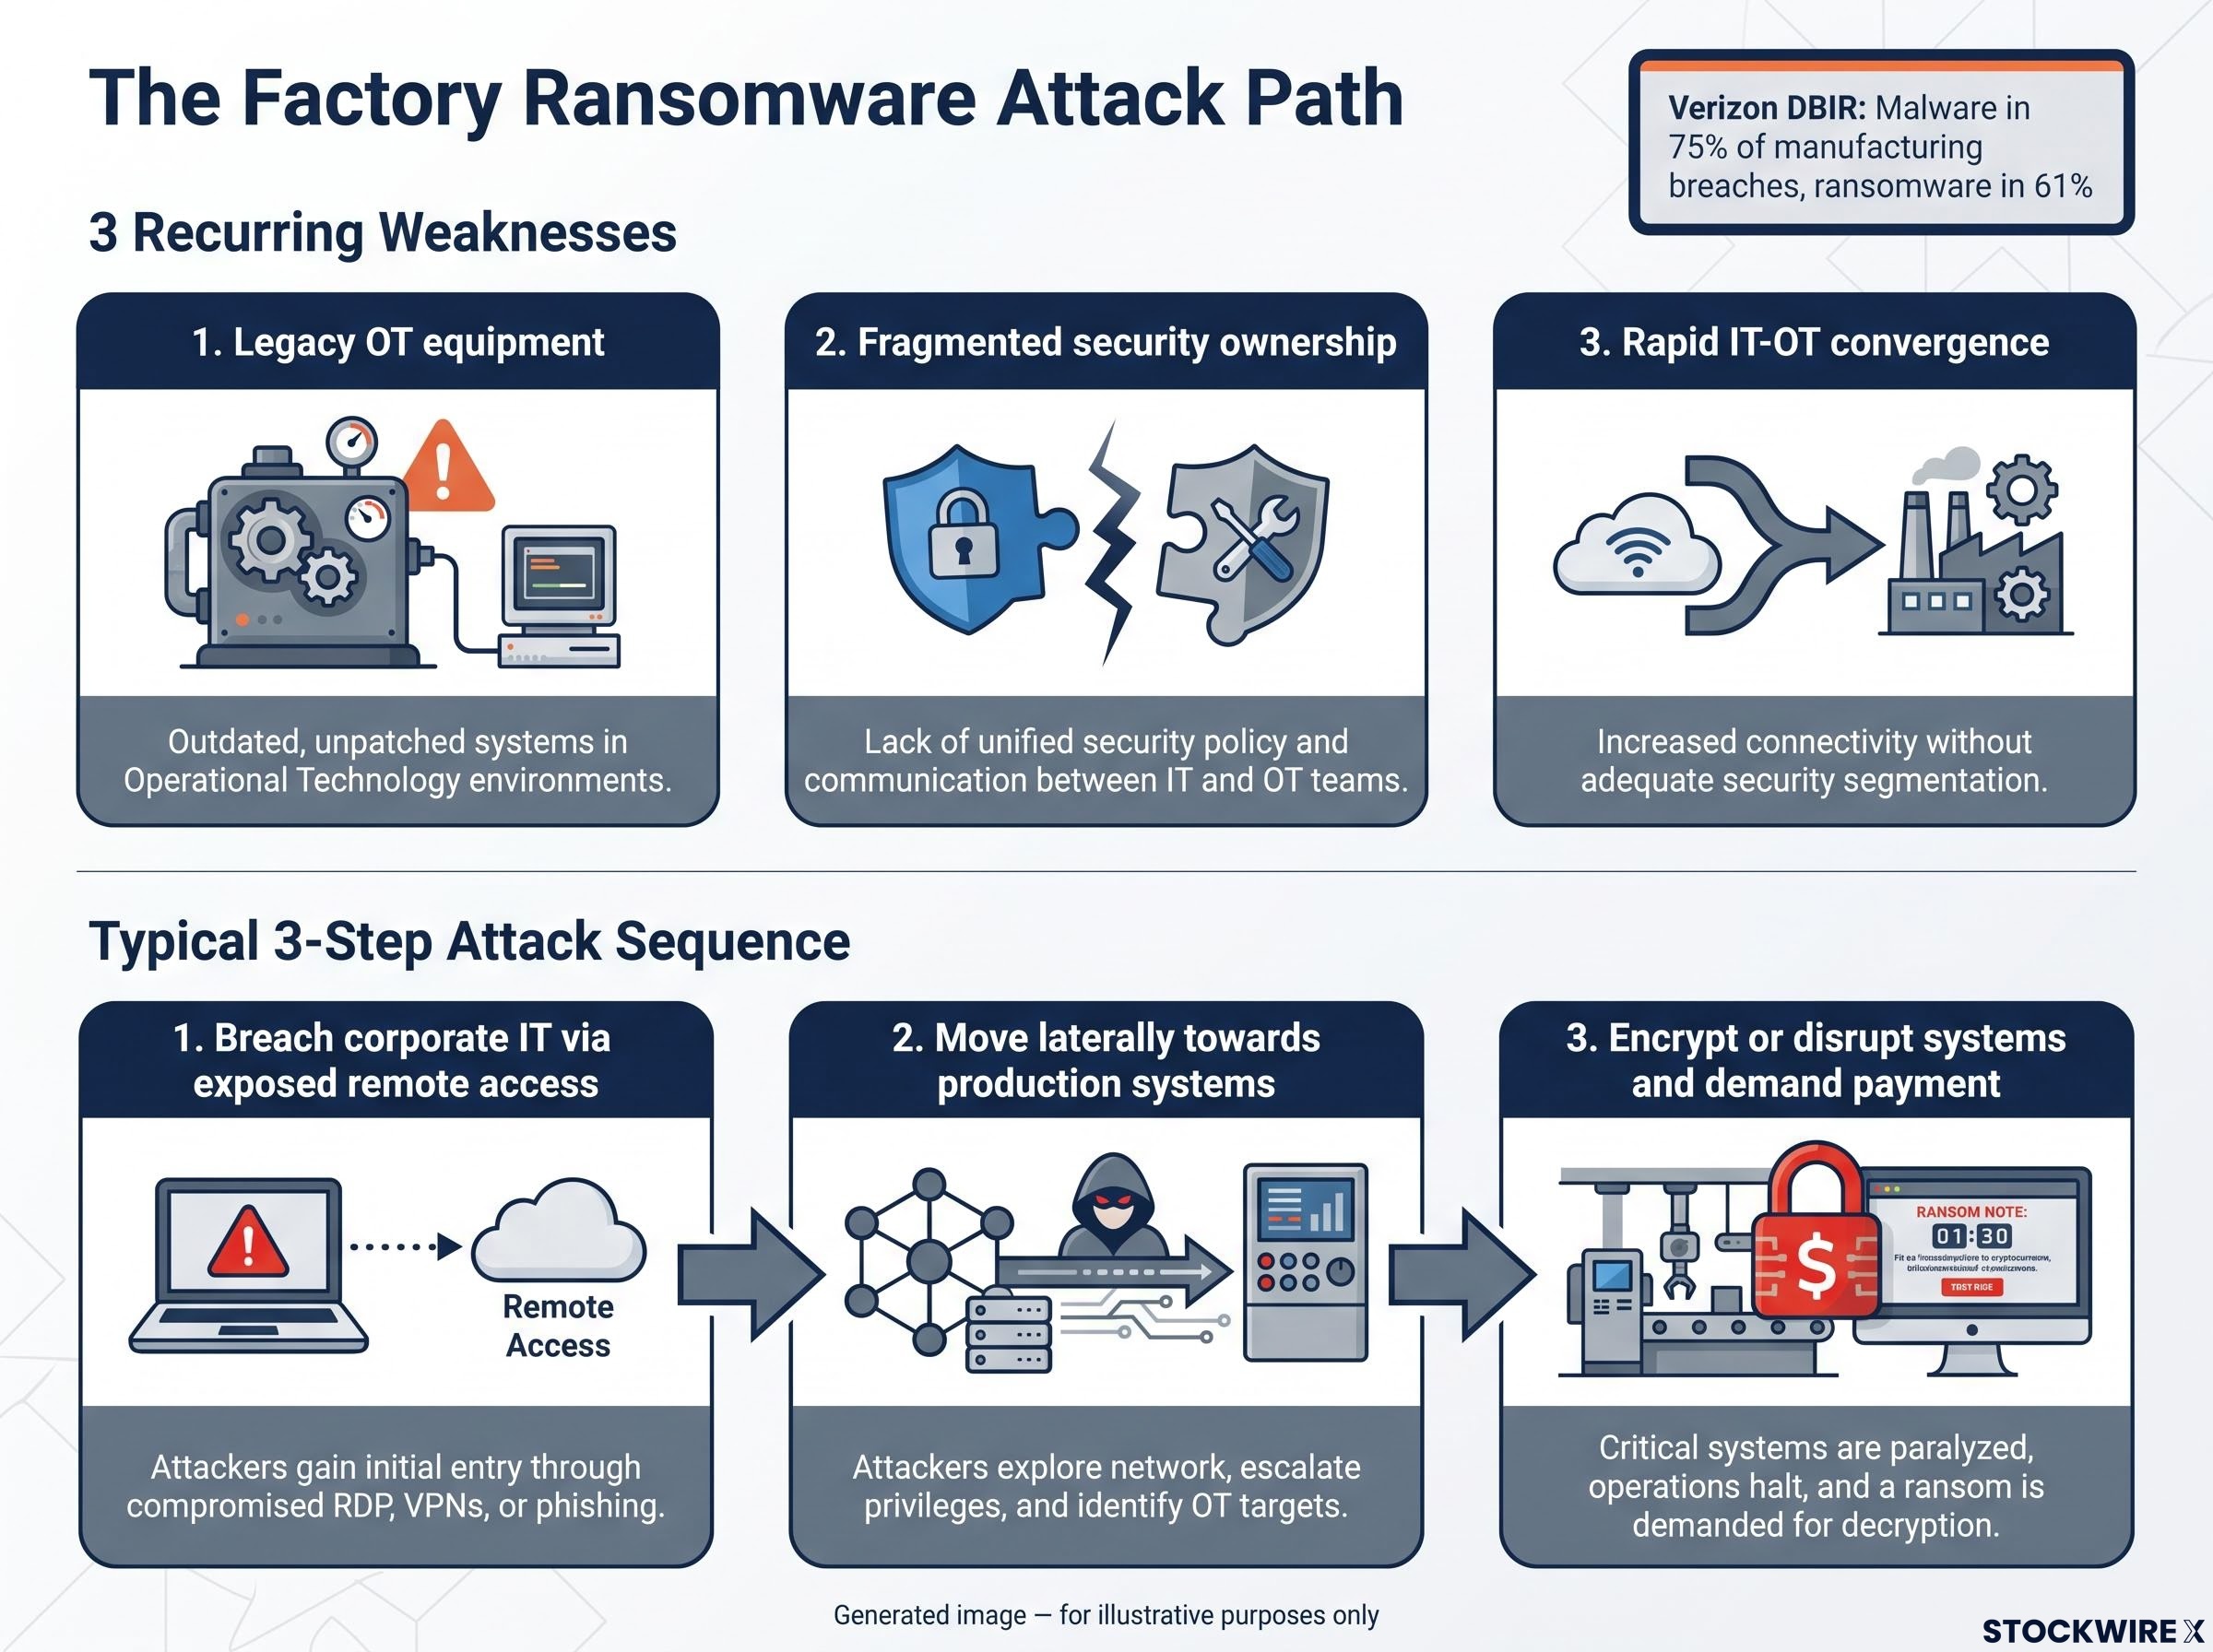
Verizon’s 2026 Data Breach Investigations Report found malware in 75% of manufacturing breaches, with ransomware in 61%. Three weaknesses keep recurring:
- Legacy OT equipment that was never designed to be patched or exposed to networks
- Fragmented security ownership between IT teams and plant engineers
- Rapid IT-OT convergence, which links corporate systems to production systems
CISA industrial control systems guidance treats critical manufacturing as a priority sector and addresses the weaknesses investors should probe, including legacy equipment, IT-OT convergence, network segmentation and secure remote access, all of which shape how exposed a plant is to an outage.
A typical attack follows a sequence:
- Attackers breach corporate IT, often via exposed remote access.
- They move laterally towards systems that connect to production.
- They encrypt or disrupt those systems and demand payment.
Dragos describes a “fundamental shift in the threat landscape,” with adversaries moving beyond pre-positioning to mapping control loops and learning to manipulate physical processes.
Two unnamed cases show the cost. A beverage maker saw attackers move from corporate IT into production, halting breweries and factories and producing a sharp drop in soft drink sales. An automaker faced a global production shutdown that included UK plants.
Names, loss figures and share-price reactions were not disclosed. Still, ransom exposure is really operational-continuity exposure, and it lands in revenue and cash flow, not an IT budget line.
Where the victims are moving: Germany, Europe and the mid-market
The geographic shift comes straight from the counts. European manufacturing victims rose 85.4%, from 199 to 369, between the first seven months of 2025 and 2026. US victims barely moved.
| Region | Jan-Jul 2025 | Jan-Jul 2026 | Change |
|---|---|---|---|
| Europe | 199 | 369 | +85.4% |
| United States | 443 | 412 | Essentially flat |
The US share of global manufacturing victims fell from 52.3% to 34.8%. That is growth elsewhere, not a US improvement.
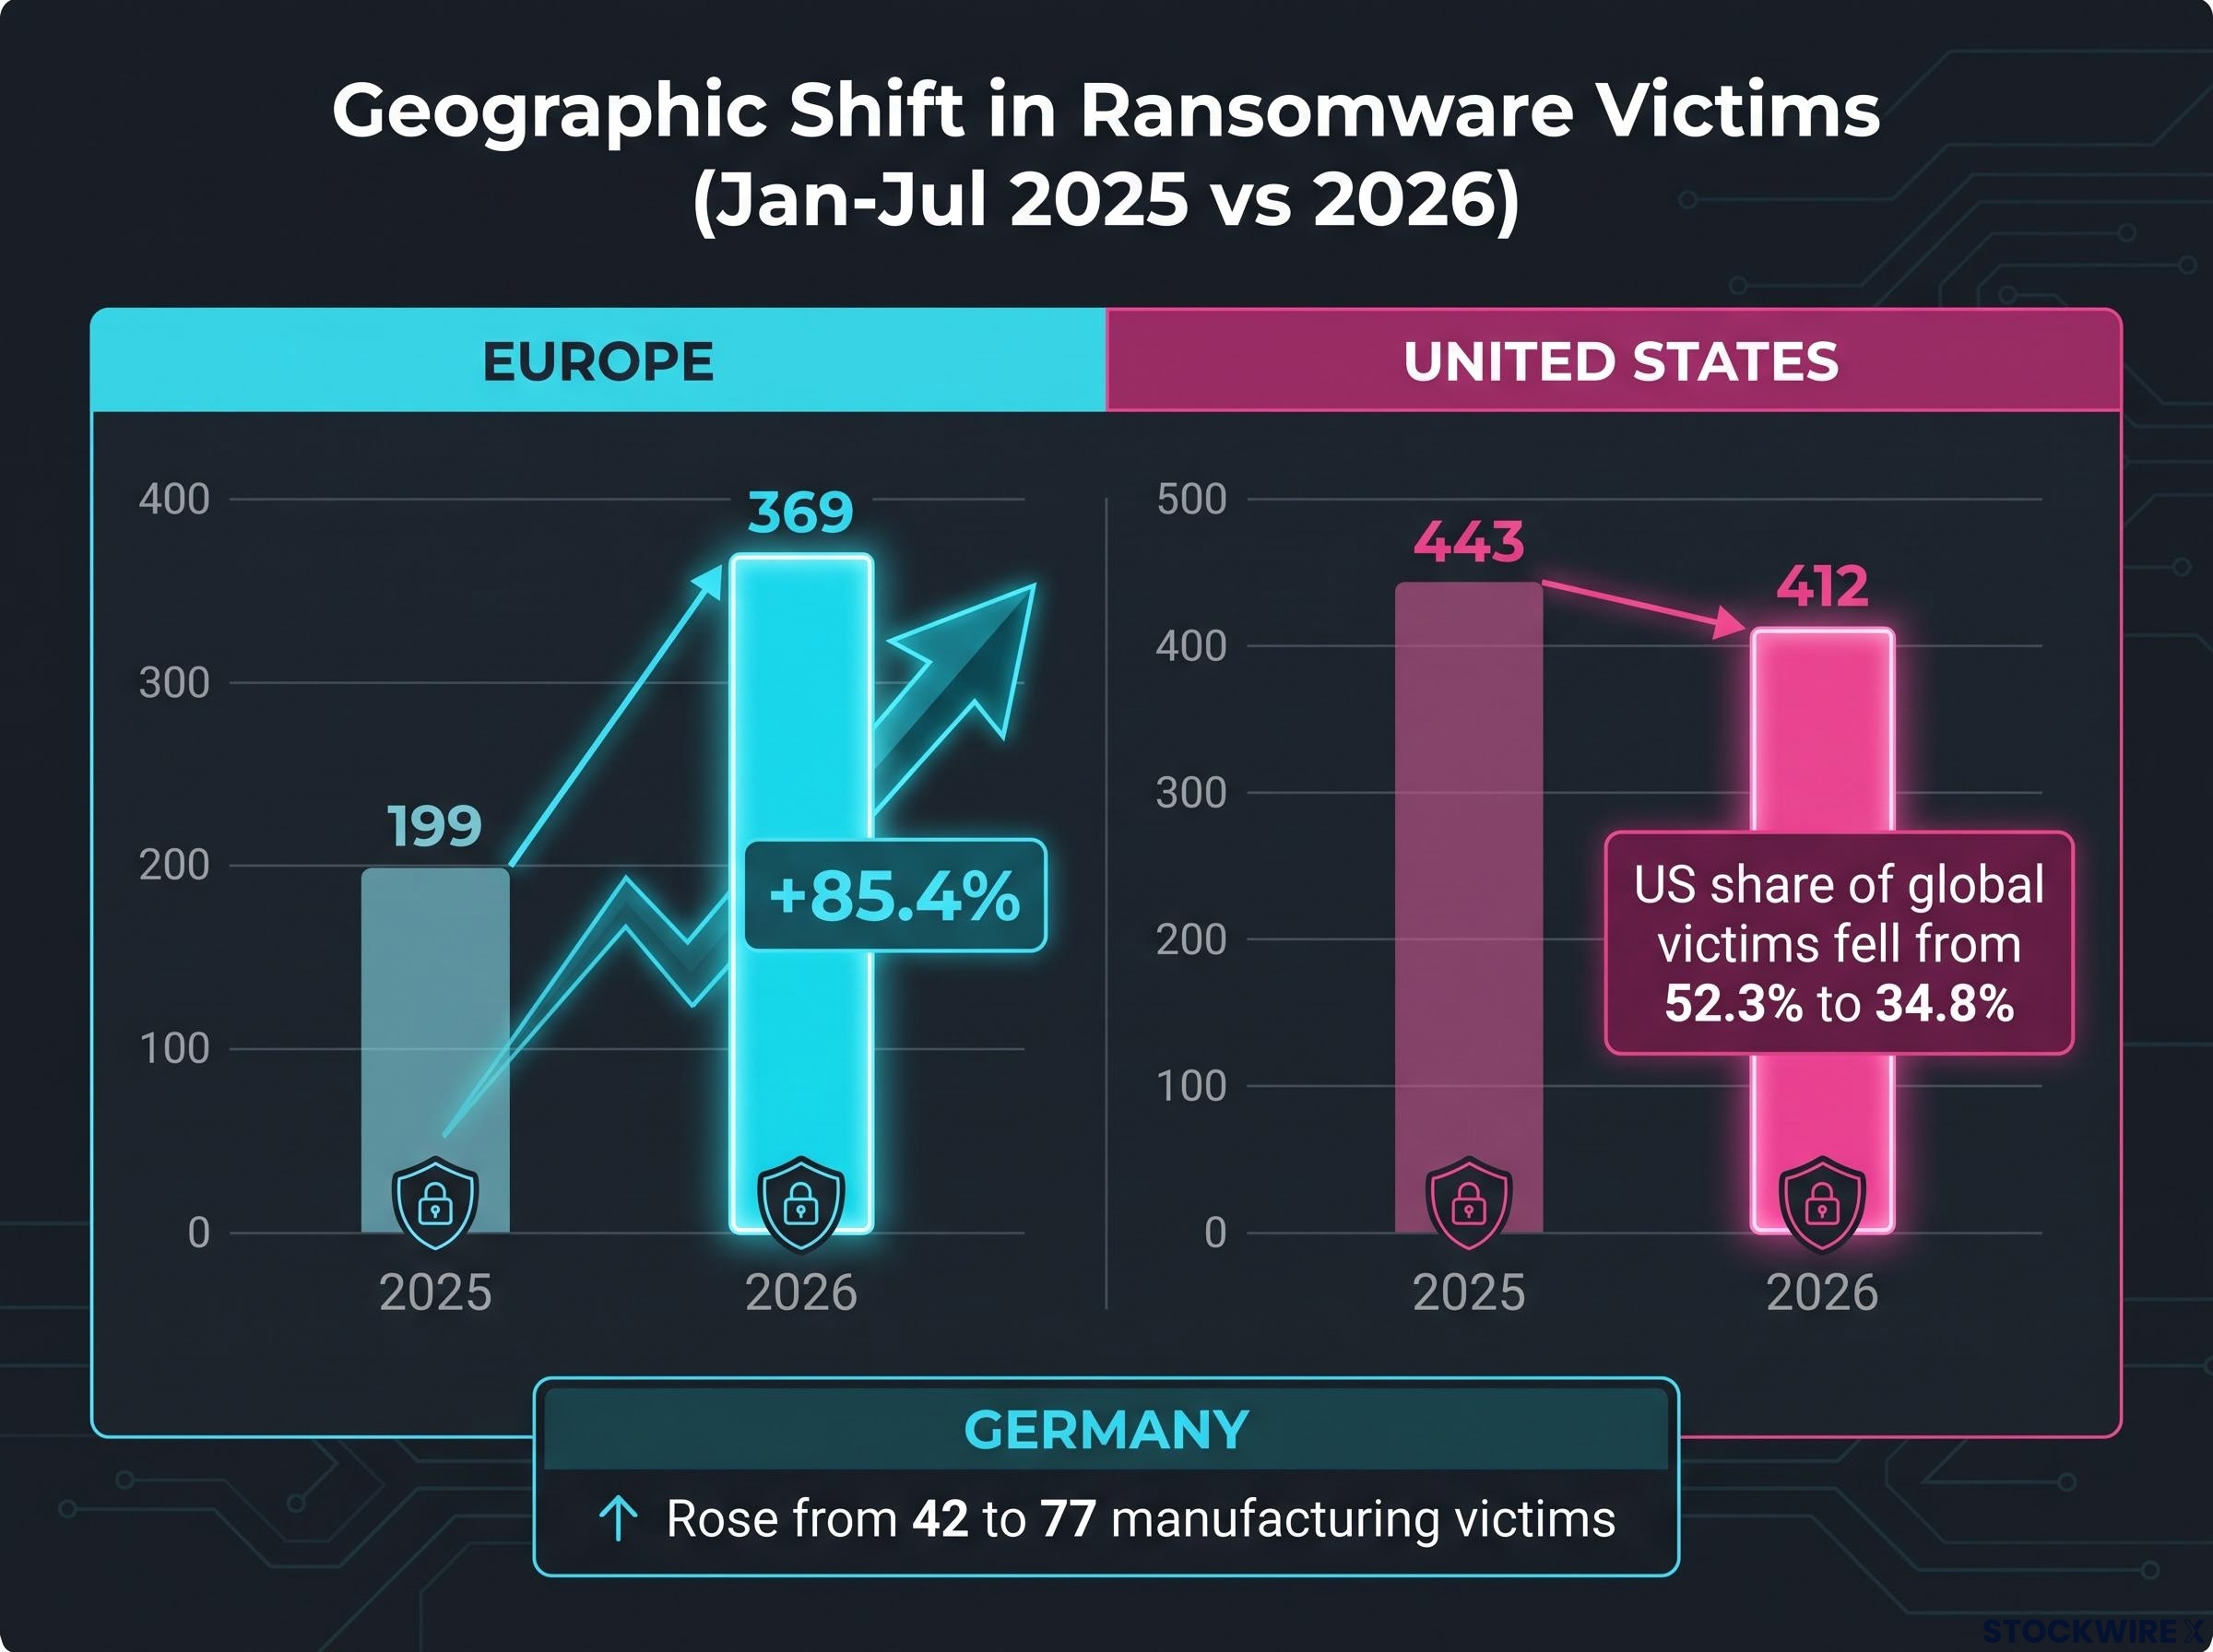
Germany leads Europe. It recorded 77 manufacturing victims against 42 a year earlier, in an economy where manufacturing is about 19.9% of output. Dragos counted German industrial incidents rising from 37 to 68 between quarters, 76% of them manufacturers.
The targets are mid-sized. The median victim has $42.9 million in revenue, 70.2% of manufacturing victims sit in the $10M-$100M band, and 73% of North American and European attacks hit mid-market firms. These companies have real revenue but thinner security budgets, and they often supply larger firms that investors do examine.
The groups behind the shift
A few operators drive the volume. Qilin leads, The Gentlemen is second, and Akira is third.
- Qilin: led manufacturing incidents in the first seven months of 2026.
- The Gentlemen: first seen in September 2025, it has 615 victims, 142 in manufacturing, and about 12% of 2026 manufacturing incidents, including 61 in Europe.
- Akira: ranked third by Black Kite and heavily focused on manufacturing in North America and Europe, per Dragos.
- SafePay: accounted for 21.9% of German manufacturing victims in 2025.
Meanwhile, 49.7% of 2026 incidents came from groups absent in 2023-2024. Because so few operators carry so much volume, one group’s change in behaviour can move short-term counts quickly.
How investors can read exposure in industrials and their suppliers
Consider the contagion logic. A small supplier stalls, and a Tier-1 manufacturer or global brand reliant on just-in-time components (parts delivered only as needed) feels it. SecurityWeek has reported that this cascade is pushing assessment towards a networked view.
Contagion through a single weak node is not unique to ransomware; semiconductor supply concentration shows how one chokepoint can ripple through technology, automotive and industrial portfolios, and investors who map supplier dependencies for cyber risk can apply the same logic to physical supply risk.
Black Kite’s Ransomware Susceptibility Index (RSI) offers an outside-in signal, measuring exposures from a vantage point similar to an attacker’s.
74.4% of victims scored above 0.4, the critical range, at disclosure. 35.1% scored 0.6 or higher, and the average was 0.552.
Black Kite argues for ranking suppliers by observable susceptibility, not revenue or date of last questionnaire. Verizon’s guidance points to IT/OT segmentation, hardened remote access and resilience planning. These five questions turn that into diligence:
- How concentrated is the company’s supplier base, and which suppliers are single points of failure?
- Are IT and OT networks segmented?
- How is remote access secured?
- Has continuity and recovery been tested?
- Has the company disclosed past incidents, and how did it respond?
What external scores cannot tell you
An outside-in score cannot see internal OT architecture, backup quality or incident-response maturity. Pair it with continuity assessments. A high score is a prompt for questions, not a verdict.
No credit rating agency or analyst quantification of valuation or credit impact was found in the research. Treat this as a qualitative framework, not a pricing model.
Reading the next quarter: signals that matter more than headline counts
The risk looks durable, relocating towards Europe and mid-sized firms, and best read through supply-chain position. Exact counts will keep shifting, but the direction has held across trackers. Three things merit watching:
- Whether Germany’s rise persists into later quarters
- Whether The Gentlemen and Qilin keep their share
- Whether rating agencies or insurers begin publishing quantified exposure
This article is for informational purposes only and should not be considered financial advice. Investors should conduct their own research and consult with financial professionals before making investment decisions. These statements are speculative and subject to change based on market developments.